SonarQube · Singapore
SonarQube in Singapore: licences, setup and training
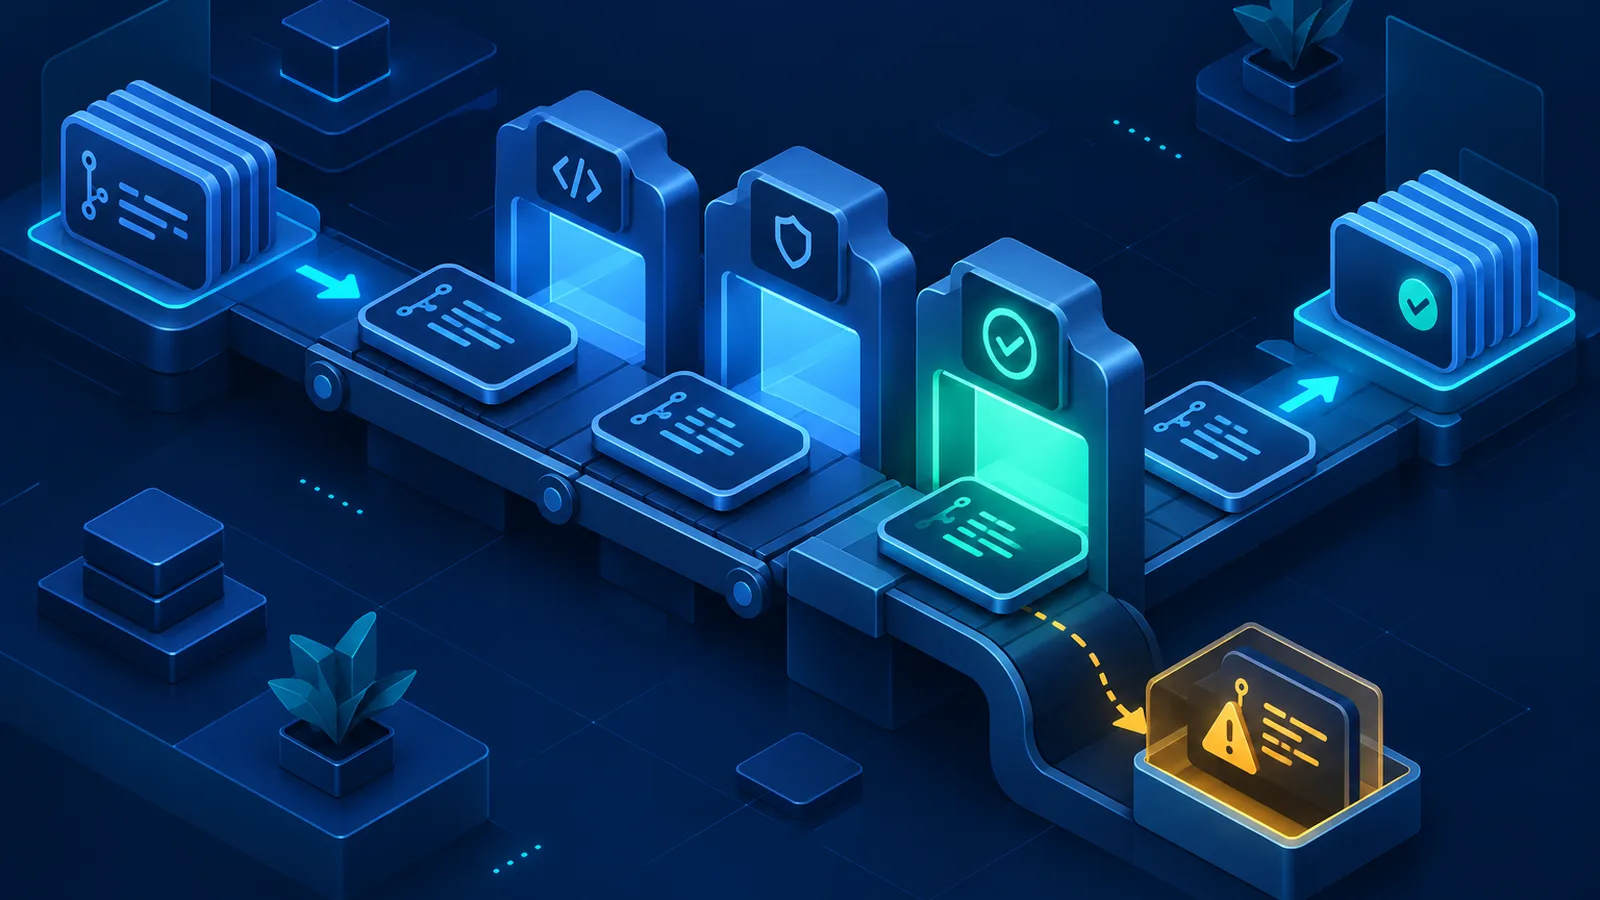
A Sonar reseller partner with an office at Suntec Tower One. We supply SonarQube licences quoted in SGD, set it up in your CI/CD pipeline, and train your developers, so code quality and security checks run on every pull request.
Buying for a Malaysian team? SonarQube Malaysia
What you get from one partner
Licences, quoted in SGD
SonarQube Team or Enterprise, as SonarQube Cloud or self-managed Server, sized to your lines of code.
Set up in your pipeline
GitHub Actions, GitLab CI, Azure DevOps or Jenkins, with quality gates your team agrees on.
Developers who act on it
Onboarding with every licence, and a hands-on workshop for teams that want to go deeper.
The SonarQube product line in Singapore
Sonar now sells more than code scanning. The full line, with the plan or edition each product needs; the last three are new.
- Platform. SonarQube Cloud: Sonar runs it for you (Team or Enterprise plan). SonarQube Server: the same checks on your own infrastructure (Developer or Enterprise edition).
- Security. SonarQube Advanced Security: deeper code scanning plus checks on open-source libraries; a separate subscription on Cloud Team or Enterprise and Server Enterprise.
- Gitar: an AI pull request reviewer that commits fixes when CI fails. A Sonar product, acquired in 2026 and sold on its own per user; we resell it and quote it alongside SonarQube.
- Sonar Vortex (new): gives your coding agent the project's rules first, then checks each change. Cloud: Sonar Agent Essentials; Server Enterprise 2026.5+.
- SonarQube Remediation Agent (new): opens checked fixes for your backlog as pull requests. Same plans as Vortex.
- SonarQube Hunter Agent (new): looks for access-control, business-logic and login flaws. Cloud Enterprise plan; Server Enterprise 2026.5+.
Team or Enterprise
Sonar sells SonarQube in two plans: Team for groups under 50 developers, and Enterprise for larger teams, with SSO and SCIM, portfolios and OWASP and MISRA reporting. The Cloud Enterprise plan is custom-priced and the self-managed Server editions are priced per instance, per year, by lines of code, so we quote after sizing your codebase.
When the free Community Build stops being enough
The Community Build analyses only the main branch. It does not analyse pull requests or post results into them, so problems surface after merge. Paid editions check every branch and pull request and report inside GitHub, GitLab, Azure DevOps and Bitbucket.
SAST tool for Singapore development teams
SonarQube is a static application security testing (SAST) tool as well as a code quality tool. From the Developer edition of SonarQube Server upwards, it runs SAST with taint analysis, secrets detection and infrastructure-as-code scanning on every branch and pull request, so a security flaw is flagged in review, not after release.
- SonarQube Advanced Security adds advanced SAST that follows untrusted data into third-party libraries, plus dependency scanning: known vulnerabilities with reachability, malicious packages, licence checks and SBOM export in CycloneDX or SPDX. It is a separate subscription on SonarQube Server Enterprise and on the SonarQube Cloud Team and Enterprise plans.
- Compliance reports on the Enterprise edition and plan, including OWASP Top 10, CWE Top 25, PCI DSS and STIG.
Agentic code fixes: SonarQube Remediation Agent
The SonarQube Remediation Agent proposes fixes for issues in your backlog and in pull requests that fail the quality gate, and opens them as pull requests. Each fix is analysed again, and a fix that fails is discarded. It covers C#, Java, JavaScript, TypeScript and Python, plus secrets. According to Sonar, it was launched globally in Singapore at ATxSummit in May 2026 and developed in partnership with IMDA.
The agent proposes fixes, but a person still approves them. See our guide to who reviews AI-generated code when coding agents open pull requests.
- On SonarQube Cloud, it comes with Sonar Agent Essentials, on the Team plan (billed annually) or the Enterprise plan.
- On SonarQube Server, it is a separate subscription on the Enterprise edition, from version 2026.5.
- We also quote Sonar Vortex, which gives a coding agent your project's context before it writes and checks each change as it goes, and the SonarQube Hunter Agent, which looks for access-control, business-logic and authentication flaws that rules miss.
- We quote the subscriptions in SGD, set the agents up on your repositories and train your developers to review what they propose.
MAS TRM source code review
MAS's Technology Risk Management Guidelines (January 2021) ask financial institutions to adopt standards on secure coding, source code review and application security testing (6.1.1). They may use a mixture of static, dynamic and interactive application security testing (6.1.6). Issues found should be tracked, and major issues and software defects remediated before production deployment (6.1.7). SonarQube supports your evidence for each of these; it does not make you compliant, and dynamic and interactive testing stay separate.
Banking in Malaysia too? Our clause-by-clause guide to RMiT source code review and the evidence to keep.
- 6.1.1, secure coding and source code review standards: quality profiles are your coding standard written down, and pull-request analysis on SonarQube Server Developer edition and up records a review of every change.
- 6.1.6, static application security testing: SAST with taint analysis and secrets detection from the Developer edition up. The Enterprise edition adds OWASP Top 10, CWE Top 25 and PCI DSS compliance reports, PDF reports and audit logs for your auditor.
- 6.1.7, track and remediate before production: a quality gate can block the merge while new major issues remain. The SonarQube Remediation Agent opens proposed fixes as pull requests, and the Hunter Agent looks for access-control and business-logic flaws; both are separate subscriptions on Server Enterprise 2026.5+.
- Third-party and open-source code (6.1.3, 6.1.4): SonarQube Advanced Security adds dependency scanning and SBOM export, as a separate subscription on Enterprise.
Cloud or Server
SonarQube Cloud is run by Sonar, with nothing to install. It stores your data in the EU by default, or in the US on the Enterprise plan; there is no Asia Pacific region, and the region cannot be changed after sign-up. SonarQube Server runs on your infrastructure when code must stay in-house, and since version 2026.5 it also runs the Remediation Agent, Sonar Vortex and the Hunter Agent in on-premise, air-gapped and VPC-restricted setups. We install, integrate and upgrade it.
Used across Singapore
Singapore's GovTech SHIP-HATS platform offers SonarQube as a managed code quality and security analysis tool that helps teams detect bugs, vulnerabilities, and code smells in their applications. Sonar's regional headquarters in Singapore, supported by the Singapore Economic Development Board (EDB), serves its growing user community and customer base across the Asia Pacific region.
Buying for a Malaysian team?
Our Malaysia page covers SonarQube licences, setup in your pipeline, and HRD Corp claimable training for Malaysian employers.
SonarQube guides
Three guides go deeper on the topics above.
Start with how SonarQube pricing works, then SonarQube Community vs Developer vs Enterprise, and finally AI Code Assurance for AI-written code.
Common questions
- How is SonarQube priced in Singapore?
- The Cloud Enterprise plan is custom-priced, and the self-managed Server editions are priced per instance, per year, by lines of code; both are quoted. We quote in SGD after you tell us your lines of code and team size.
- How are lines of code counted?
- On SonarQube Cloud, only private projects count; SonarQube Server counts every analysed project. Both count only the largest branch of each project, and analysis frequency does not change the count.
- Should we choose SonarQube Cloud or Server?
- Cloud if you want nothing to maintain; Server if code must stay on your own infrastructure. We quote both.
- Do you provide SonarQube training in Singapore?
- Yes. Onboarding is included with every licence, and we run a hands-on workshop for your developers on request.
- Are you a SonarQube partner?
- We are a Sonar reseller partner serving Singapore and Malaysia, supplying licences together with setup and training.
- Is SonarQube a SAST tool?
- Yes. From the Developer edition of SonarQube Server upwards, SonarQube runs static application security testing (SAST), including taint analysis, secrets detection and infrastructure-as-code scanning, on every branch and pull request. SonarQube Advanced Security extends it with advanced SAST into third-party libraries and dependency scanning.
- Is SonarQube Advanced Security included in Enterprise?
- No. Advanced Security is a separate subscription, available on SonarQube Server Enterprise and on the SonarQube Cloud Team and Enterprise plans. We quote it in SGD alongside your licence.
- Can we run the Remediation Agent on-premise in Singapore?
- Yes. Since SonarQube Server 2026.5 LTA (September 2026), the Remediation Agent, Sonar Vortex and the Hunter Agent run on self-managed SonarQube Server Enterprise, including on-premise, air-gapped and VPC-restricted deployments, with your own LLM through Azure AI Foundry, AWS Bedrock or a custom gateway. Each is a separate subscription, which we quote in SGD.
SonarQube quote · Singapore
Get a SonarQube quotation in SGD
Name the plan or edition you are looking at, and any add-ons such as Advanced Security or the Remediation Agent. Not sure yet? Tell us your lines of code and we will size it. Quoted in SGD by Anchor Sprint Pte. Ltd., with GST shown on the quotation where it applies.
Advanced Security, the Remediation Agent, Sonar Vortex and the Hunter Agent quoted with your licence.
Sized to your lines of code, usually within two working days.
Setup in your pipeline and onboarding for your developers, itemised.
More for Singapore
Get SonarQube checking every pull request
Tell us your team size, lines of code and CI platform. We will recommend a plan and quote licences, add-ons, setup and training in SGD, with GST shown where it applies.
Anchor Sprint Singapore
7 Temasek Boulevard, #12-07 Suntec Tower One
Singapore 038987
Fax: +65 6917 8977
Anchor Sprint Pte. Ltd. · UEN 202632732Z