Team
For teams under 50 developers
- Finds bugs, vulnerabilities and security hotspots across 30+ languages on every pull request
- 14-day free trial, no credit card
SonarQube Malaysia · Sonar reseller partner
We are a Sonar reseller partner in Malaysia. We supply SonarQube licences, set it up in your CI/CD pipeline, and train your developers to act on what it finds, so code quality and code security checks run on every pull request instead of after release. That includes Sonar's new AI agents: Sonar Vortex, the Remediation Agent and the Hunter Agent.
Buying for Singapore? See SonarQube Singapore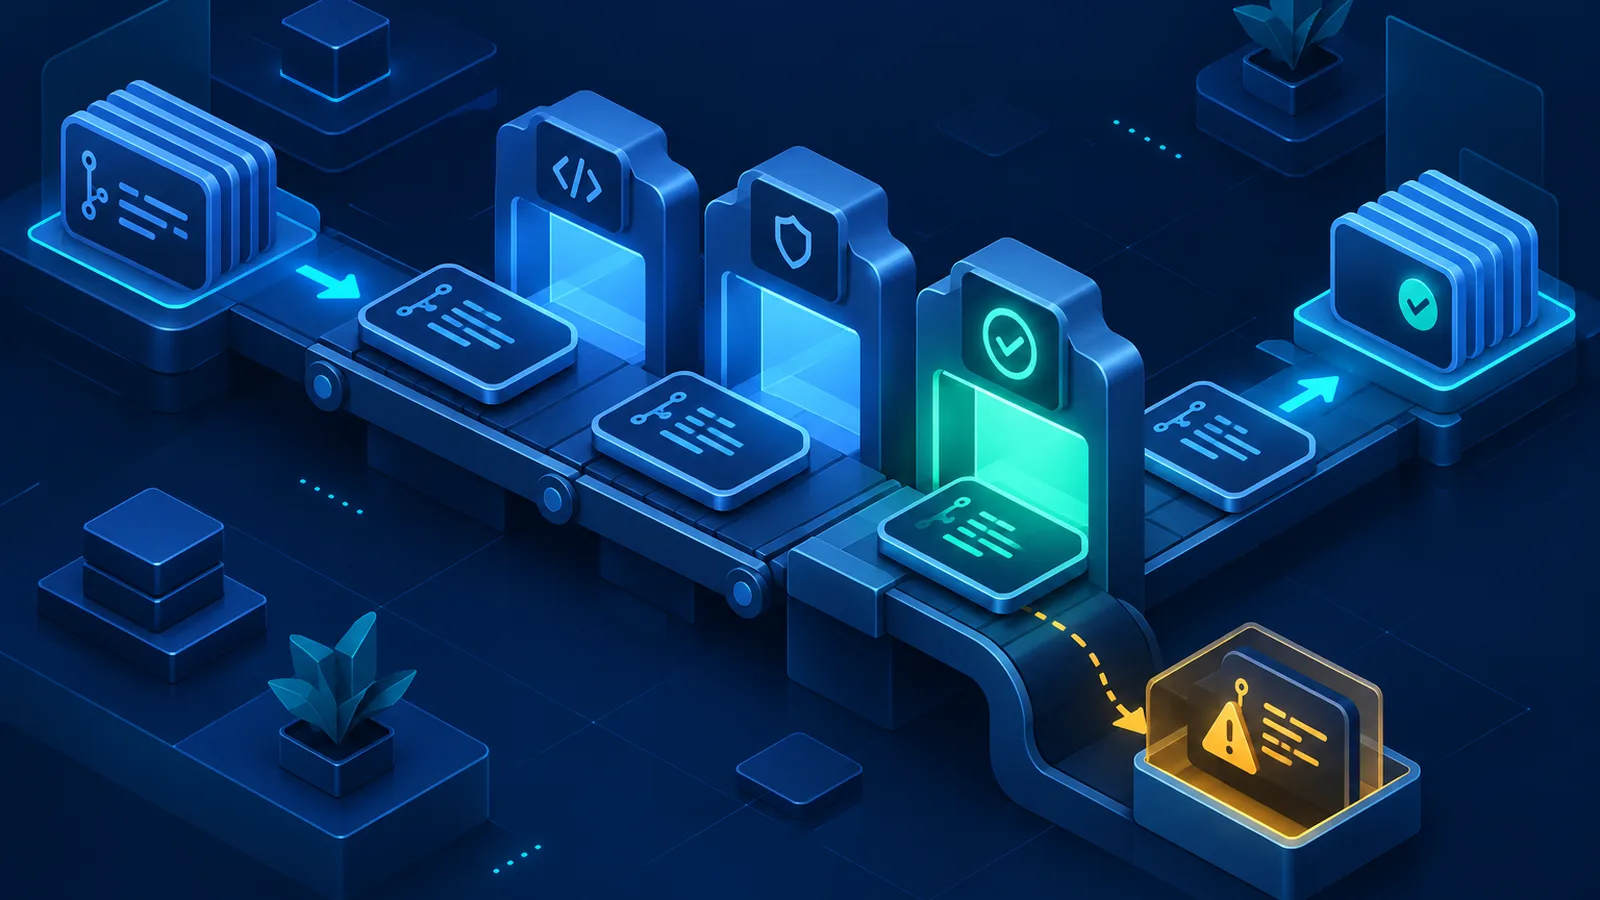
Product line
Sonar now sells more than code scanning. Here is the full line, grouped the way a buyer compares it, with the plan or edition each product needs. We quote SonarQube licences and add-ons in Ringgit.
"New" follows Sonar's own product menu. Sonar Agent Essentials is available on the SonarQube Cloud Team plan billed annually, or on the Enterprise plan. Gitar is a Sonar product that Sonar acquired in 2026; we resell it and quote it alongside SonarQube.
Security and AI agents
Most of Sonar's security and agent products sit on the Enterprise edition or a paid Cloud plan. Some are included; others are separate subscriptions that we quote alongside your licence.
Reviews each pull request, works out why a CI run failed, and commits a fix; on the Pro plan it repeats until CI passes.
A Sonar product, acquired by Sonar in 2026. Sold on its own per user (Core, Pro and Enterprise plans) and also offered with SonarQube and Advanced Security. We resell it and quote it alongside SonarQube.
Gives a coding agent your project's context before it writes, then checks each change as it is made, before a pull request exists.
Cloud: with Sonar Agent Essentials on the Team plan (billed annually) or the Enterprise plan. Server: separate subscription on Enterprise, version 2026.5 or later.
Proposes fixes for backlog issues and failing pull requests and opens them as pull requests; a fix that fails re-analysis is discarded.
Same plans as Sonar Vortex. On Cloud you connect your own LLM API key.
Looks for broken access control, business-logic and authentication flaws that rules miss, on a schedule or on demand, and reports only what it can confirm.
Cloud Enterprise plan only. Server: separate subscription on Enterprise, version 2026.5 or later.
Advanced SAST that follows untrusted data into third-party libraries, plus dependency scanning: known vulnerabilities with reachability, malicious packages, licence checks and SBOM export.
Separate subscription on SonarQube Server Enterprise and the SonarQube Cloud Team and Enterprise plans. Not available on Developer.
Suggests a fix, generated by a large language model, for an issue SonarQube has found.
Included in SonarQube Server Enterprise and the SonarQube Cloud Team and Enterprise plans. Not in Developer.
Reports against OWASP Top 10, CWE Top 25, PCI DSS, STIG, MISRA and the EU Cyber Resilience Act, for auditors and clients.
Included in SonarQube Server Enterprise and the SonarQube Cloud Enterprise plan.
Since SonarQube Server 2026.5 LTA (September 2026), the three agents also run on self-managed Server Enterprise, including on-premise, air-gapped and VPC-restricted setups, with your own LLM. Sonar publishes no Server prices, and neither do we: tell us which add-ons you need and we quote them with your licence.
Ask for an Enterprise quote with the add-ons you needSAST
SonarQube is a static application security testing (SAST) tool as well as a code quality tool. On SonarQube Server, from the Developer edition up, it runs taint analysis, secrets detection and infrastructure-as-code scanning on every branch and pull request, so a security flaw is caught in review rather than after release.
SAST for banks
Bank Negara Malaysia's RMiT policy document asks for source code reviews on changes to critical systems, static and dynamic testing of APIs, and a secure development lifecycle from the vendors who build them. PCI DSS asks for custom software to be reviewed before release. SonarQube supports your evidence for each of these; it does not make you compliant, and your auditor still decides.
For banks, insurers and payment firms we lead with SonarQube Server Enterprise, self-managed, so code and analysis results stay on your own infrastructure. SonarQube Cloud stores data in the EU or the US only and has no Asia Pacific region. SonarQube Advanced Security is the standard add-on, for the dependency and SBOM evidence.
Source code reviews on changes to critical systems, before the change goes live
Pull-request analysis and a quality gate that blocks the merge; the analysis history is the per-change record
Developer edition and up
Automated security compliance review and vulnerability discovery for DevOps teams
SAST with taint analysis and secrets detection on every branch and pull request
Developer edition and up
Periodic static and dynamic security testing of APIs
SAST on your API code covers the static part; dynamic and penetration testing stay separate
Developer edition and up
Vendors show a secure development lifecycle in due diligence
OWASP Top 10 and CWE Top 25 compliance reports, PDF and regulatory reports, and audit logs
Enterprise edition
Vetting of third-party and open-source software; an SBOM
Dependency scanning and SBOM export in CycloneDX or SPDX
Enterprise + Advanced Security add-on
Custom software reviewed before release; automated review is allowed
Pull-request quality gate, plus the PCI DSS compliance report
Gate: Developer and up. Report: Enterprise
Defences against business-logic and access-control attacks
SonarQube Hunter Agent, which looks for broken access control, business-logic and authentication flaws
Server Enterprise 2026.5+, separate subscription
An inventory of custom software and third-party components
SBOM export from Advanced Security, once per release
Enterprise + Advanced Security add-on
To close findings before release, the SonarQube Remediation Agent opens proposed fixes as pull requests for your reviewers (a separate subscription on Server Enterprise 2026.5+). Raise audit-log retention before an audit period: default housekeeping deletes entries monthly. RMiT references are to the policy document issued on 25 September 2026. This is not legal advice.
SonarQube plans
Sonar packages SonarQube in two plans. We follow the same structure, so what you compare on Sonar's site is what we quote.
Team
For teams under 50 developers
Enterprise
For teams over 50 developers
Sonar lists SonarQube Cloud Team from US$34/month for up to 100k lines of code, currently shown as a discounted rate, so check it before you budget (checked on Sonar's pricing page, September 2026). The Cloud Enterprise plan and all self-managed Server editions are quoted: tell us your lines of code and we will size it.
SonarQube Cloud is run by Sonar. Nothing to install or upgrade; you connect GitHub, GitLab, Bitbucket or Azure DevOps.
SonarQube Server runs on your own infrastructure (Developer or Enterprise edition). Choose it when code must stay in-house; we install, integrate and upgrade it for you.
Many teams start on the free Community Build. It analyses only the main branch: it does not analyse feature branches or pull requests, and it cannot post results into your pull requests. Problems are found after the code is merged.
Enable
A licence is only useful once SonarQube is part of how your team ships. Enablement is included in every deployment.
GitHub Actions, GitLab CI with merge-request decoration, Azure DevOps pipelines and Jenkins.
Gates your team agrees on, tuned so they block real problems instead of blocking every build.
SSO, permissions and project structure mapped to how your teams are organised.
Migration from an existing Community Build instance, keeping your history and settings where possible.
For Server, we plan and run version upgrades so you stay on a supported release.
Free. We connect VS Code, JetBrains, Visual Studio or Cursor to your server's rules in connected mode, so developers see issues before they commit.
Free. Lets coding agents such as Claude Code and Cursor read SonarQube issues and quality gates, so agent-written code is checked against the same rules.
Train
Every licence includes onboarding for your developers. For teams that want to go further, we run a hands-on workshop on reading SonarQube results, fixing issues and working with quality gates. For Malaysian companies, the workshop can be claimed through HRD Corp.
Sonar's AI Code Assurance applies dedicated quality gates to AI-generated code, so code from an assistant or agent is held to rules your team can read and change. It runs from the Developer edition up. If your team writes code with AI assistants, pair it with Sonar Vortex while the agent writes and the Remediation Agent for the backlog it leaves.
When agents open more pull requests than your reviewers can read, see who reviews AI-generated code, layer by layer, from Gitar on the pull request to the approval only a person can give.
Questions
Sonar lists SonarQube Cloud Team from US$34/month for up to 100k lines of code, currently shown as a discounted rate, so check it before you budget. The Cloud Enterprise plan is custom-priced, and the self-managed Server editions are priced per instance, per year, by lines of code; both are quoted. Tell us your total lines of code and team size and we will send a quotation.
On SonarQube Cloud, only private projects count; SonarQube Server counts every analysed project. Both count only the largest branch of each project. How often you run analysis does not change the count.
Cloud suits teams who want nothing to install or maintain. Server suits teams that must keep code on their own infrastructure. We can quote both and help you decide.
It analyses only the main branch. It does not analyse feature branches or pull requests, and it cannot show results inside your pull requests. Paid editions add both.
We are a Sonar reseller partner in Malaysia and Singapore. We supply SonarQube licences and provide setup and training alongside them.
Our SonarQube team workshop can be claimed through HRD Corp by Malaysian employers. Onboarding is already included with every licence we supply.
On SonarQube Server, standard commercial support is available on every edition, Developer included, at additional cost; it is included in Enterprise plans from 30M lines of code. 24/7 premium support is available on Enterprise. We itemise support options in your quote, and we handle setup, integration and first-line questions for the teams we supply.
AI CodeFix is included in SonarQube Server Enterprise and in the SonarQube Cloud Team and Enterprise plans; it is not in the Developer edition. The Remediation Agent is a separate subscription: on Cloud it comes with Sonar Agent Essentials on the Team plan (billed annually) or the Enterprise plan, and on Server it needs the Enterprise edition, version 2026.5 or later. We quote the edition and the agent subscription together.
No. Advanced Security is a separate subscription, on SonarQube Server Enterprise and on the SonarQube Cloud Team and Enterprise plans. Core SAST, taint analysis and secrets detection are already in SonarQube Server from the Developer edition up; Advanced Security adds dependency scanning, SBOM export and advanced SAST into third-party libraries.
Sonar sells three agents: Sonar Vortex, which guides and checks a coding agent while it writes; the SonarQube Remediation Agent, which opens fixes for your backlog as pull requests; and the SonarQube Hunter Agent, which looks for logic and access-control flaws. Each is a separate subscription. On SonarQube Cloud, Vortex and the Remediation Agent come with Sonar Agent Essentials (Team plan billed annually, or Enterprise) and the Hunter Agent needs the Enterprise plan. On SonarQube Server, all three need the Enterprise edition, version 2026.5 or later. As a Sonar reseller partner we quote them in Ringgit with your licence and set them up on your repositories.
Yes, as one control among several. Pull-request analysis and quality gates (Developer edition and up) support your evidence for source code reviews on changes to critical systems under RMiT S 10.10. The Enterprise edition adds compliance, PDF and regulatory reports and audit logs for due diligence, and the Advanced Security add-on exports an SBOM. SonarQube does not make you compliant, and dynamic and penetration testing stay separate. Banks usually run SonarQube Server Enterprise self-managed, because SonarQube Cloud has no Asia Pacific data region.
Gitar is an AI pull request reviewer that Sonar acquired in 2026. It reviews pull requests and commits fixes when CI fails. It is a separate Sonar product, sold on its own per user and also offered with SonarQube and Advanced Security; it is not included in a SonarQube licence. We resell it and quote it alongside SonarQube.
Send us your team size, lines of code and CI platform. We will recommend a plan and quote licences, setup and training together.
Get a SonarQube quote